Cold wallets are no longer an absolutely secure option.
Author: Azuma,Odaily Planet Daily
Cold wallets, which have always been regarded as the "safest way to store cryptocurrency," are no longer safe.
On the evening of October 9th, blockchain detective Specter reported that multiple reports of Ledger users' wallets being stolen had surfaced on X and Reddit. After tracing the relevant addresses, Specter discovered thatthese addresses had received funds from hundreds of wallets across several major blockchains, including Ethereum, TRON, and Bitcoin, with total losses exceeding $86 million.
From supply chain anomalies to suspected hardware implantation, where did the problem lie?
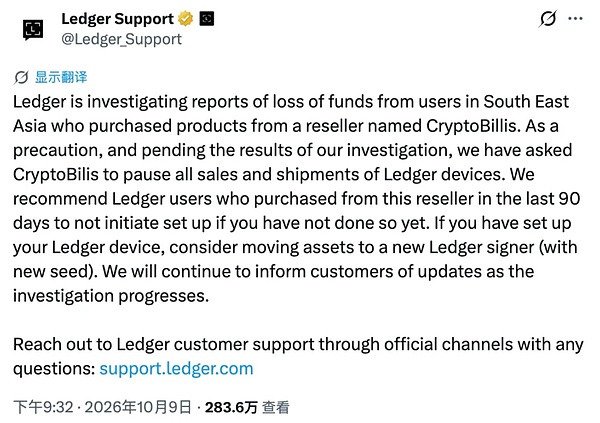
Following the theft, Ledger immediately issued a statement pointing the investigation to a reseller called CryptoBilis.
Ledger stated that it is investigating an asset theft incident involving users in Southeast Asia who had previously purchased devices through the reseller CryptoBilis.Ledger has requested the reseller to suspend sales and shipments and advises users who purchased devices through this channel within the past 90 days not to initialize their devices. Users who have already completed setup should create a new Ledger signing device using the new mnemonic phrase and transfer their assets to the new wallet.
More specific clues came from former Mt. Gox CEO Mark Karpelès. As early as October 8, Karpelès warned that counterfeit or tampered Ledger devices with hidden SIM cards were being sold on the market, and these SIM cards could transmit stolen mnemonic phrases.
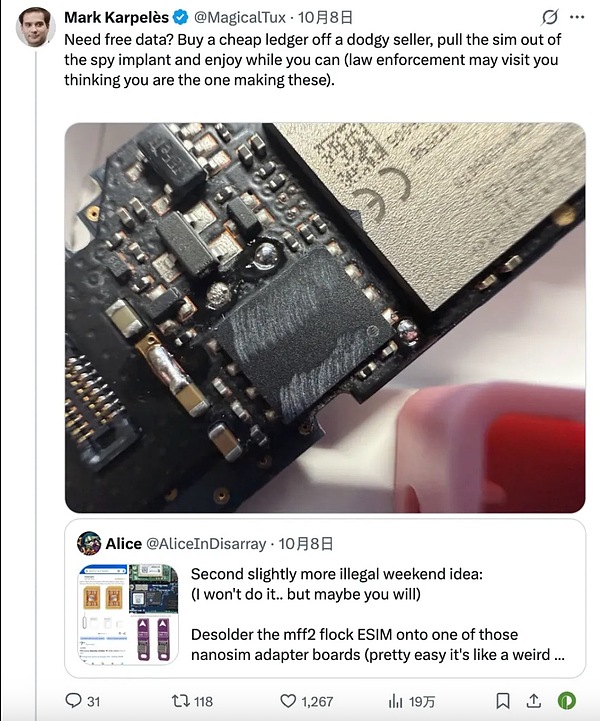
Following the incident,Karpelès further disclosed that the Ledger hardware wallet she purchased from Malaysia had intact outer packaging, but a suspicious module with a SIM card chip was hidden under the screen pad.
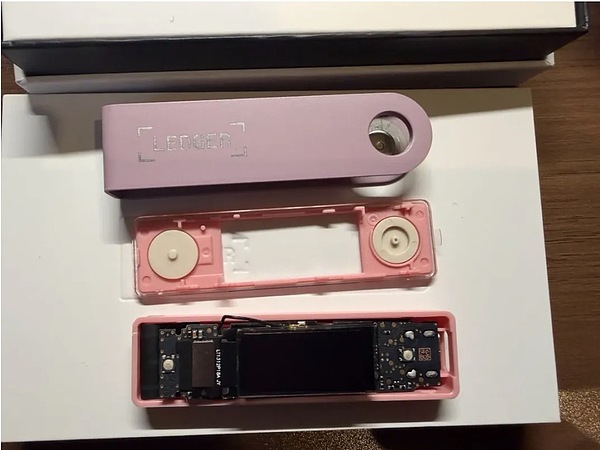
Based on this, 23pds, Chief Information Security Officer of SlowMist, speculated that attackers may intercept data displayed on the device screen through malicious modules, record recovery phrases when users initialize their wallets or view their mnemonic phrases, and then transmit the information via LTE or eSIM.
The danger of this type of attack lies in its potential to bypass users' conventional understanding of hardware wallet security.While the security elements of a hardware wallet can protect private keys from direct reading, they may not prevent external hardware from intercepting screen information.In other words, even if the core security elements are not compromised, physical tampering with the device can still lead to the leakage of the mnemonic phrase.
However, the aforementioned attack mechanism remains a technical speculation, and the specific cause of this security incident requires further verification. Another viewpoint suggests that the attackers chose to act yesterday precisely because Karpelès' warnings were gradually spreading, and the attackers, fearing their operations had been exposed, began their actions.
If this attack path is ultimately confirmed, then this incident will expose not only the security problem of a particular wallet, but a more fundamental risk: how secure can self-hosting be when users cannot be sure that the hardware in their hands remains trustworthy from the factory to delivery?
Lamborghini, confidentiality restrictions, change of ownership... CryptoBilis is shrouded in mystery.
As the investigation deepened, the background of the distributor involved, CryptoBilis, gradually came to light.
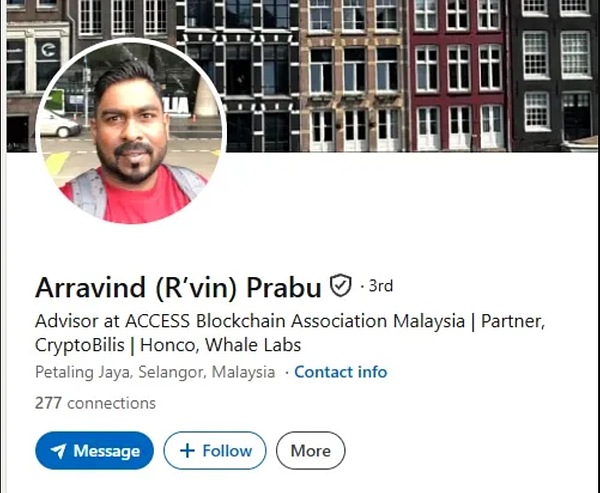
CryptoBilis is a Web3 e-commerce and self-custody tool vendor based in Petaling Jaya, Malaysia, offering products such as hardware wallets. According to public information, the company was co-founded by Arravind Prabu, who serves as CEO, and Vimal Selvamany, who serves as CTO.
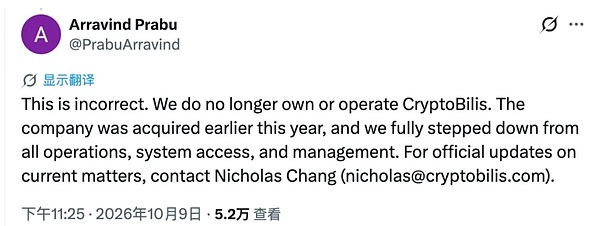
However, after the incident drew attention, Arravind Prabu quickly clarified on X that claims that he was still operating CryptoBilis were inaccurate. The company had been acquired back in March of this year, and the original management team had relinquished all operational, administrative, and system privileges. Regarding the current situation, he suggested contacting a current person in charge, Nicholas Chang ([email protected]).
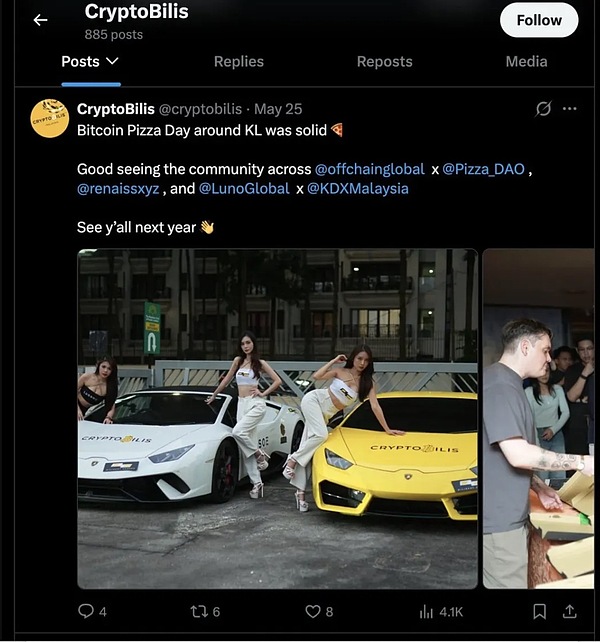
Community users then continued to press for answers, asking why there had been no official announcement before the company had changed hands, and why the account's most recent post even featured a Lamborghini... Arravind Prabu responded thatthe post was made by the new management team, and that the original team, due to confidentiality clauses in their contracts, had to wait until October 19th to publicly announce the transaction, and that they currently had no access to the company's account, backend, and operating systems.
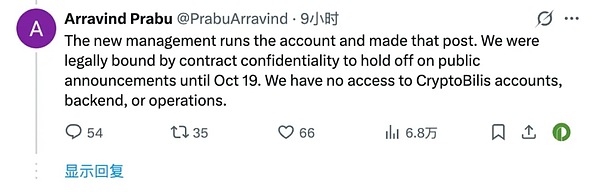
The former CEO has publicly stated that the original management team has stepped down from operations; however, there is still a lack of independently verifiable information regarding what actually happened within the company after the handover.
Another, more attention-grabbing clue comes from the company's equity. Bitcoin News disclosed after the incident that relevant equity transfer records showed thatan individual named JIAMING, registered in Heilongjiang Province, China, had held 100% of CryptoBilis's shares since August 3.
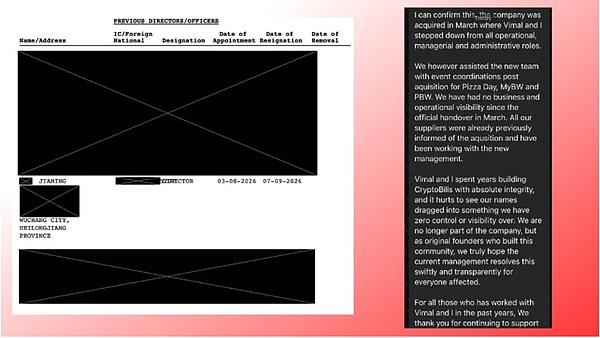
This means that,at least based on publicly available information, CryptoBilis did indeed change hands several months before the suspected supply chain attack.However, there is currently no conclusive evidence to confirm the specific details of the shareholding change, the actual operations of the new management, or whether the new shareholders are related to the equipment in question. The new shareholders' registered address or the acquisition date cannot be used to directly link them to the theft.
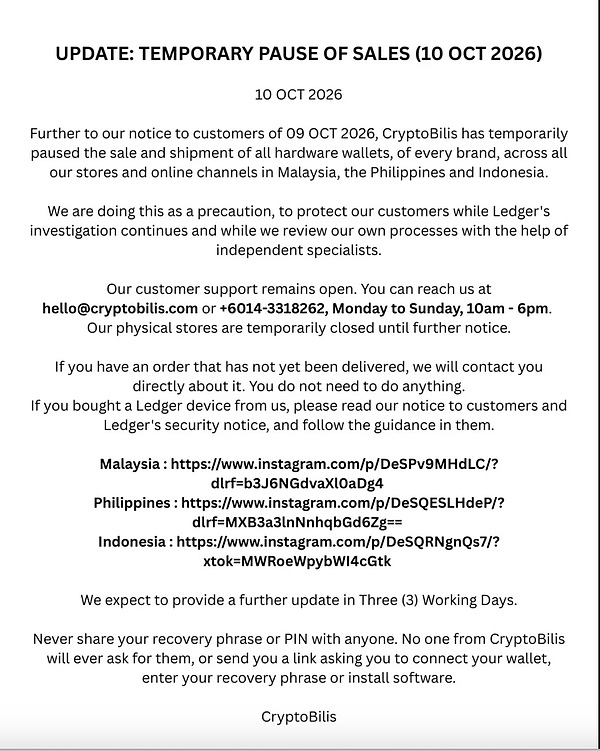
In response to the investigation, CryptoBilis has publicly announced via its official X account that it is suspending the sale and shipping of its hardware wallets through all stores and online channels in Malaysia, the Philippines, and Indonesia, and its physical stores are temporarily closed. The company stated that this move is to cooperate with the Ledger security incident investigation and to allow for independent expert review of its internal processes; outstanding orders will be handled proactively by customer service, and further developments are expected to be announced within three business days.
As of this writing, the most critical questions remain unanswered—at which stage was the equipment tampered with, was the original supply chain exploited, and can the current management team provide sufficient records to reconstruct the delivery process? These questions await answers from subsequent investigations and disclosures.
Individual loss case: A wealthy individual had just bought a wallet a week ago...
Based on current on-chain tracking, the losses from this incident are not only staggering in scale, but the flow of funds also exhibits different characteristics.
According to Galaxy Research Director Alex Thorn, the estimated Bitcoin loss related to the Ledger and CryptoBilis supply chain incident is 213.42 BTC, equivalent to approximately $17.7 million at the time. Of this, about 92% of the Bitcoin was held for less than 90 days when it was collected. The tracked BTC remains unspent and is held in three collection addresses.
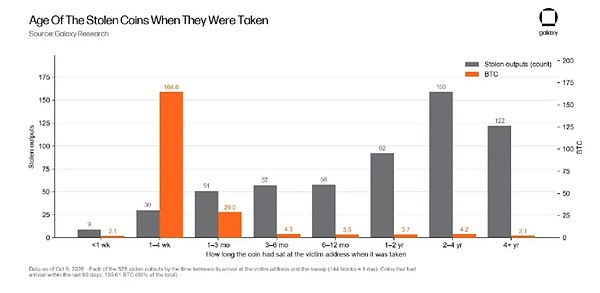
The losses suffered by individual victims are even more alarming. Lookonchain monitoring indicates thata user with the address TY24Ya purchased a Ledger device three weeks ago and subsequently deposited 7 million USDT into their wallet, but this money was all transferred out within approximately 10 hours. Another user bought 80 BTC for approximately $5.2 million four months ago, at one point making a floating profit of approximately $1.38 million, but after purchasing a Ledger device from CryptoBilis a week ago and transferring all their BTC into the device, they ultimately suffered a total loss.
Is it possible to recover the funds?
Shortly after the incident, the attackers quickly began the money laundering and mixing process.
Onchain analytics firm Onchain Lens reports thata suspected attacker deposited 430.2 ETH, worth approximately $1.07 million, into Tornado Cash through four wallets in an attempt to sever the tracing link on the Ethereum blockchain.
Meanwhile, the industry has begun to "contain" the attackers' stolen funds.Tether has frozen some of the USDT related to this incident, but the hackers' response was equally cunning and professional. After Tether took action, they quickly used the SUN.io and USDD PSM mechanisms of the TRON ecosystem to instantly exchange the unfrozen USDT for the more censorship-resistant decentralized stablecoin USDD. Some of the transfers also involved Binance's hot wallet (which may become clues for identifying the hackers later).
Currently,the key to asset recovery lies in the ability to promptly identify and intercept funds that remain on centralized platforms or in frozen stablecoin addresses. Assets thathave already entered coin mixing protocols, cross-chain transfers, or other complex paths may face even greater difficulties in tracking and recovering them.
As of now, Ledger has not released a complete fund recovery plan, nor has it disclosed any compensation arrangements for victims. As the investigation progresses, whether the assets can be recovered and who will bear the responsibility remain to be confirmed.
Cold wallets are no longer a completely secure solution.
Cold wallets have long been considered one of the most reliable self-custody solutions for crypto assets, with Ledger being the most representative brand in this market. Compared to exchange custody, users keeping their own private keys is intended to reduce reliance on third parties. However, this incident raises a disturbing question—if a user's purchased device is physically tampered with before delivery, even if the packaging is intact and core security components are not compromised, the assets may still be at risk.
Of course, the specific attack path of the incident has not yet been confirmed, and this cannot negate the overall security of hardware wallets. However, it at least reminds users that security depends not only on the device itself, but also on the purchase channel, the initialization process, and the way the mnemonic phrase is stored.
When risks can originate at the source of the supply chain, even the seemingly safest self-managed solutions can fail. This time, it truly caught everyone off guard.
Source:Global Cybersecurity Alliance (GCSA)
Website:www.gcsa.org
Get updates in your inbox
We respect your privacy. See our Privacy Policy